Control Over Personal Data Now Has a Clear Legal Foundation
For years, personal data protection in Indonesia was scattered across sector-specific regulations that often overlapped. That changed when Law Number 27 of 2022 on Personal Data Protection was enacted on 17 October 2022. The law gave data controllers a two-year transition period to adjust, so its provisions have applied in full since October 2024. One of the most important parts of the Personal Data Protection Law (UU PDP) is its recognition of data subject rights, meaning the rights of individuals whose data is processed by others. For the general public, this is the part most worth understanding.
Who Is the Data Subject and Who Is the Data Controller
The PDP Law distinguishes between several roles in data processing. The data subject is the individual the data belongs to, while the data controller is the party that decides the purpose and means of processing that data. A data controller can be a private company, a government agency, an organization, or in certain contexts even an individual. The distinction matters because legal obligations attach to the data controller, while rights attach to the data subject. In other words, when someone asks for their data to be deleted or corrected, that request is directed at the controller responsible.
The Right to Correct and Update Data
Data subjects have the right to ask controllers to complete, update, or correct errors and inaccuracies in their personal data. This right can look simple, but its impact can be significant. Incorrect data in financial, employment, or public service systems can harm a person over the long term. Outdated information that keeps circulating can also cause misunderstandings, such as an old address or a job title that no longer applies. With this legal basis in place, data subjects no longer have to rely on the goodwill of system operators to fix mistakes.
The Right to Delete and Destroy Data
The right people look for most often is the right to end processing and to have personal data deleted or destroyed. The PDP Law allows data subjects to request this in accordance with applicable laws and regulations. In practice, the right becomes relevant when data is no longer needed for the purpose it was originally collected for, when consent has been withdrawn, or when processing has been carried out unlawfully. There are exceptions, of course, such as data that must be retained under other legal obligations or for law enforcement purposes. For that reason, every deletion request should be drafted with a clear argument and reference to the appropriate legal basis.
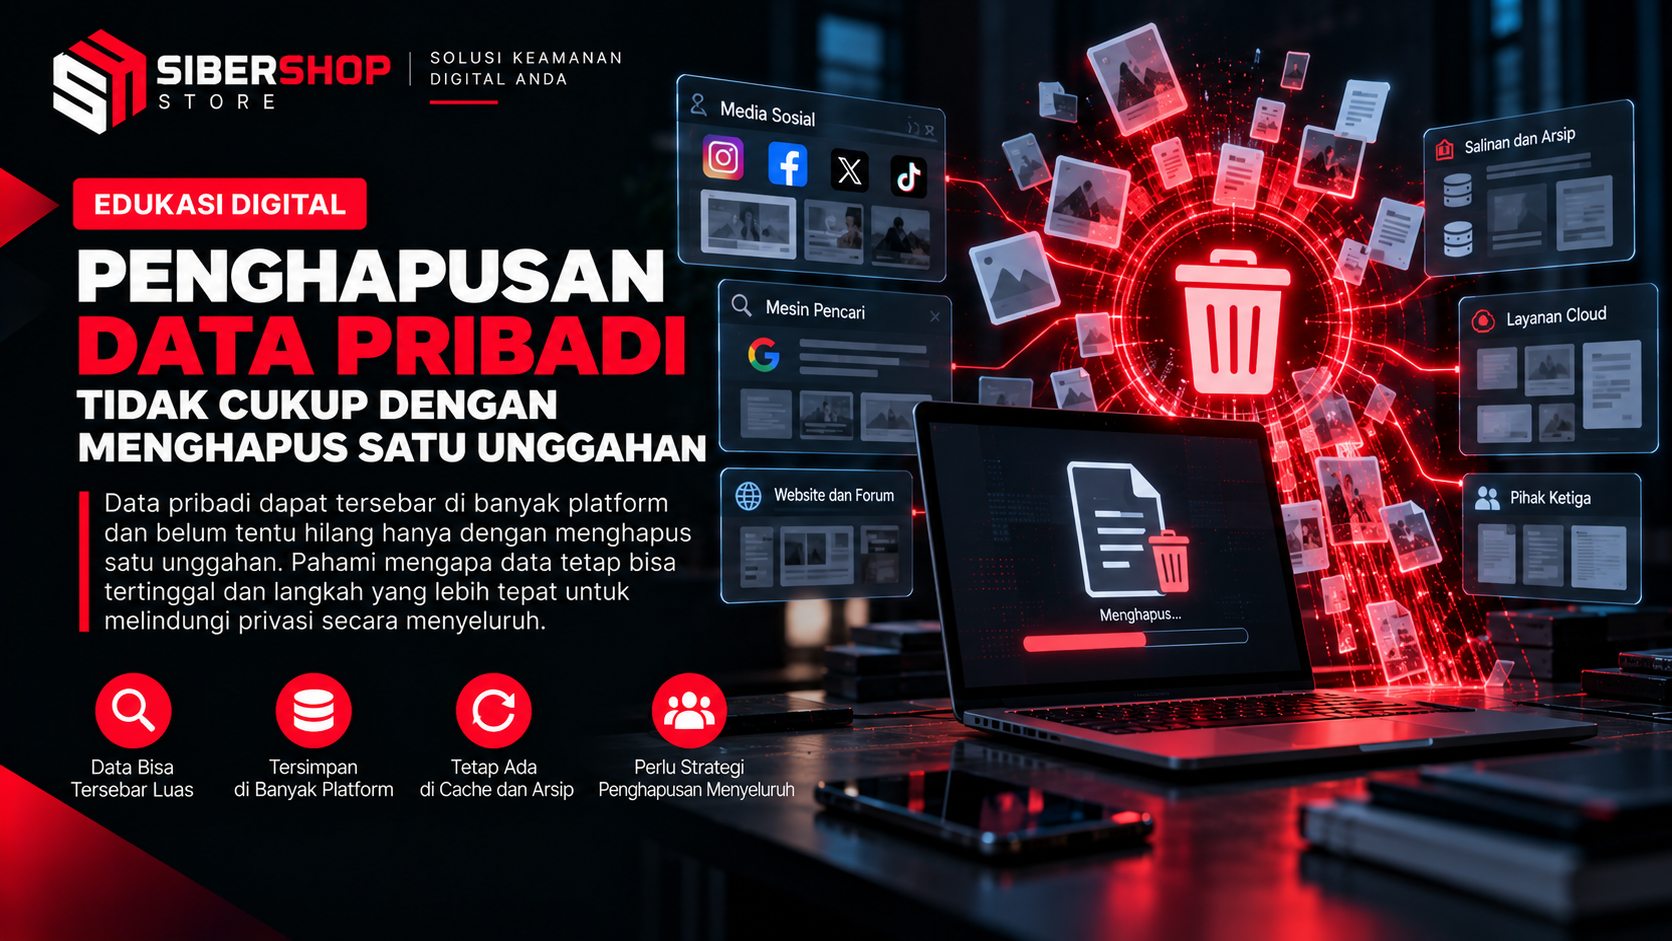
It is also worth noting that the right to deletion does not automatically mean the information disappears from the entire internet. The right applies to the specific data controller processing that data. If the data has already been copied by other parties, a request needs to be submitted to each of them. Understanding this helps data subjects set realistic expectations and plan a more effective strategy.
The Right to Withdraw Consent
Consent is one of the most common legal bases for processing data. Many services ask users for consent at sign-up, often through a checkbox that gets ticked without being read. The PDP Law makes clear that data subjects have the right to withdraw consent they have previously given. Once consent is withdrawn, the data controller must stop any processing based on that consent within the prescribed time frame. This right brings new balance to a relationship between users and service providers that has long been one-sided.
Beyond these three rights, the PDP Law also covers others, including the right to information about the purpose of processing, the right to access a copy of one's data, the right to object to decisions made solely through automated processing, and the right to sue and receive compensation for violations in data processing. Taken together, these rights form a fairly complete framework. A legal framework only matters, however, if people use it. Many are not yet aware these rights exist, let alone how to exercise them.
Challenges in Exercising Data Subject Rights
In practice, exercising data subject rights still runs into a number of obstacles. Not every data controller provides an official channel for receiving requests, and some respond slowly or not at all. Platforms based overseas also have their own procedures and legal interpretations. Data subjects often struggle to work out who a request should go to and what evidence is required. As a result, many requests stall halfway.
This is why a well-prepared legal approach matters. Requests that cite the relevant articles, clearly identify the data in question, and include adequate documentation generally receive more serious attention. Siber Group supports this process through its legal channel reporting service, from case analysis and drafting formal requests to follow-up with data controllers and the platforms involved. This kind of support helps data subjects exercise their rights without having to navigate complicated procedures on their own.
Another point to keep in mind is that data subject requests should be documented from the outset. Records of when a request was sent, to whom, and how it was answered become very useful if the process needs to be escalated. This documentation also serves as evidence if a data controller fails to meet its obligations within a reasonable time. Without careful records, data subjects will find it hard to show that their rights have been ignored. This simple habit is often what separates a successful request from one that goes nowhere.
Data subjects also need to assess clearly which data is most urgent to deal with. Data that creates security risks, such as a home address, an ID number, or financial information, generally deserves priority. Less sensitive data can be handled gradually. Setting priorities helps limited effort deliver the most meaningful results. A planned approach is always more effective than sending requests to every party at once without a strategy.
Implications for Individuals and Organizations
For individuals, the PDP Law is a tool for regaining control over personal information that has long seemed out of reach. For organizations, it is a reminder that customer and employee data is not an asset to be handled however they please. Companies that take data subject requests seriously will build stronger trust. Conversely, ignoring data subject rights exposes them to administrative sanctions and reputational damage. Both sides benefit when these rights and obligations are well understood.
Since taking full effect in October 2024, the PDP Law has changed how personal data is viewed in Indonesia. Cultural change does not happen overnight, but the policy direction is clear. Everyone now has a legal basis to ask questions, request corrections, and demand the deletion of data that should not be processed. Understanding these rights is the first step, and using them carefully is the next.
Contact Us
Contact us through Siber Group's official channels for a confidential initial consultation.