Dozens of Indonesian Army Subdomains Allegedly Hacked Simultaneously; Incident Occurred on July 27, 2026
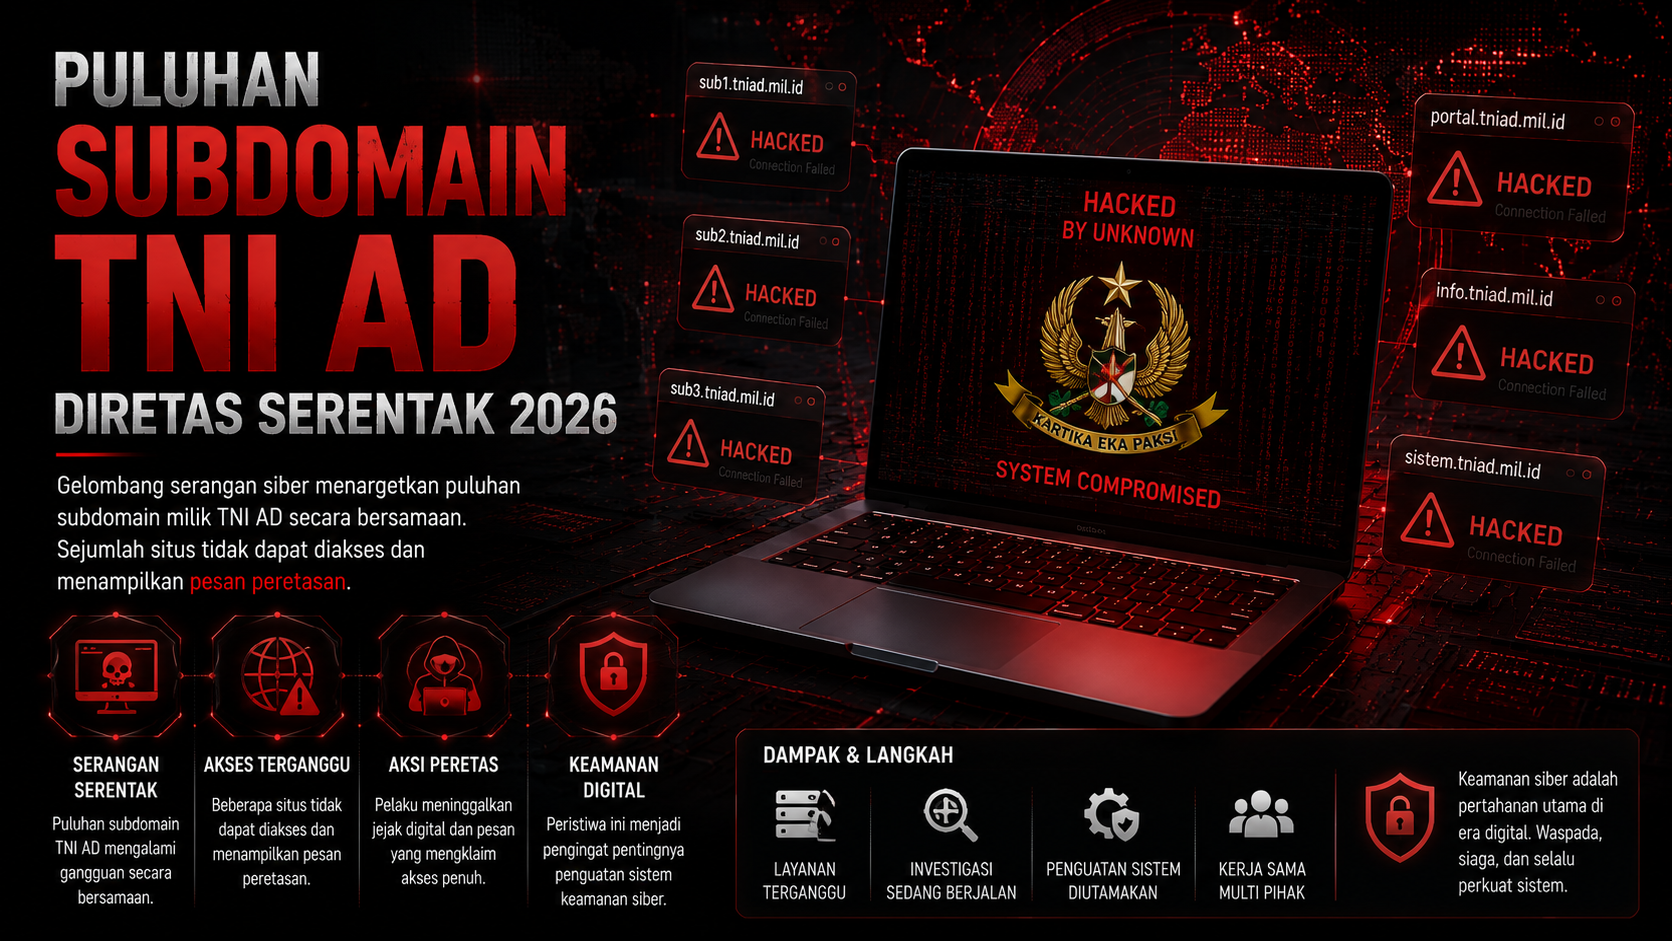
The national cybersecurity landscape has once again been shaken by reports of a mass defacement incident targeting a number of official subdomains belonging to the Indonesian Army (TNI AD). Based on monitoring data published on Monday, July 27, 2026, the Zone-XSec defacement archive noted that dozens of subdomains under the tni-ad.mil.id domain experienced changes to their page appearance almost simultaneously. The affected sites belong to various units, ranging from Kodim and Kodam to Komlekdam, indicating that the scope of this incident is quite broad and not limited to a single unit. As of the publication of this report, the Indonesian Army has not issued an official statement regarding the incident.
This defacement is claimed to have been carried out by an actor using the alias azraelzer0d4y, a name previously linked to a number of similar incidents in various countries. Interestingly, this incident occurred shortly after DailyDarkWeb, an account that monitors dark web activity, posted a claim regarding an alleged data breach said to be linked to the mabesad.mil.id domain. In the post, the threat actor in question claimed to have obtained a number of databases, server configurations, system accounts, and even WordPress credentials used on several services within the Indonesian Army. To date, there has been no technical evidence or official confirmation directly linking the alleged credential leak to the defacement incidents recorded on Zone-XSec.
Attack Patterns and Risks Behind Mass Defacement
Cybersecurity experts generally explain that large-scale defacement attacks like this typically occur when multiple sites share the same infrastructure, have similar security vulnerabilities, or experience compromises of administrator accounts or website management panels. In the case of large institutions with tens to hundreds of active subdomains, a single vulnerability in a centrally managed content management system can affect many sites at once. This is why such incidents are often referred to as chain attacks, where a single vulnerability serves as an entry point for exploiting dozens of other domains within the same ecosystem.
It is important to understand that defacement essentially only alters the appearance of a site’s homepage and does not automatically imply that a data breach has occurred. However, the occurrence of this incident alongside claims of credential leaks from other sources remains a red flag that warrants further investigation. Confirmation of whether data or credentials have been stolen can only be established through a comprehensive digital forensic investigation of all affected systems, including access logs, administrator login histories, and activity traces on the servers hosting those subdomains.
A Real Threat to Institutions with Multiple Digital Domains
This case serves as a reminder to every institution—whether government, military, or private—that maintaining numerous active subdomains entails far more complex monitoring requirements than managing a single website. Any subdomain that is not monitored regularly has the potential to become an entry point for malicious actors, especially if it uses an outdated CMS version, unpatched plugins, or weak administrator credentials that are reused across multiple services. Incidents like this are also often triggered by human factors, such as credentials leaked through phishing, password-stealing malware, or the habit of using the same password across various internal systems.
From a reputational standpoint, the impact of mass defacement incidents like this extends far beyond the altered appearance of a website. Coverage of the incident on various news platforms and defacement archives—such as Zone-XSec—also shapes public perception of an institution’s readiness to address cyber threats. The longer an incident is left without an official clarification, the more room there is for speculation and negative narratives to spread in the digital space, which can ultimately affect public trust in the institution in question.
Common Mitigation Steps
When facing such incidents, the first step is typically to isolate the affected subdomain to prevent the exploit from spreading to other systems that are still secure. After that, a thorough audit of all active subdomains is crucial, including checking software versions, server configurations, and revalidating all access credentials. It is also essential to ensure that restoring the site from a clean backup does not contain the same vulnerabilities, as restoration without patching security vulnerabilities will only open the door to repeated attacks in the future.
In addition to technical recovery, institutions facing similar incidents generally also need to address their digital footprint and the circulating news coverage, given that information regarding such incidents can persist for a long time on search engines and in public archives. A comprehensive response—covering both the technical aspects of system security and the management of public information—is key to ensuring that the incident does not drag on and does not cause additional harm in the future.